TryHackMe | Advent of Cyber 2022 *Get started with Cyber Security in 24 Days - learn the basics by doing a new, beginner-friendly security challenge…*tryhackme.comhttps://tryhackme.com/room/adventofcyber4")[](https://tryhackme.com/room/adventofcyber4)
Another day, Another challenge. This one is based off OSINT (Open Source Intelligence). In a nutshell, OSINT means gathering of information from publicly available sources and for this challenge our main goal is to help elf Recon that is ElfMcRed to gather as much information as possible about the domain santagift.shop using OSINT. Let’s get to solving now.
Q1. “What is the name of the Registrar for the domain santagift.shop?”
To solve this question we’ll be using a technique called as whois lookup. What is whois lookup? It’s basically gathering information about an ip or domain. There are alot of whois lookup tools available but the one we’ll be using for this task is https://who.is/whois . Make sure you load up this site. Now in the search bar just search the domain given and after you hit search, wait don’t get overwhelmed by the amount of information displayed. After clicking the search button if you look through the output given you should end up finding the exact information we are supposed to give to ElfMcRed.
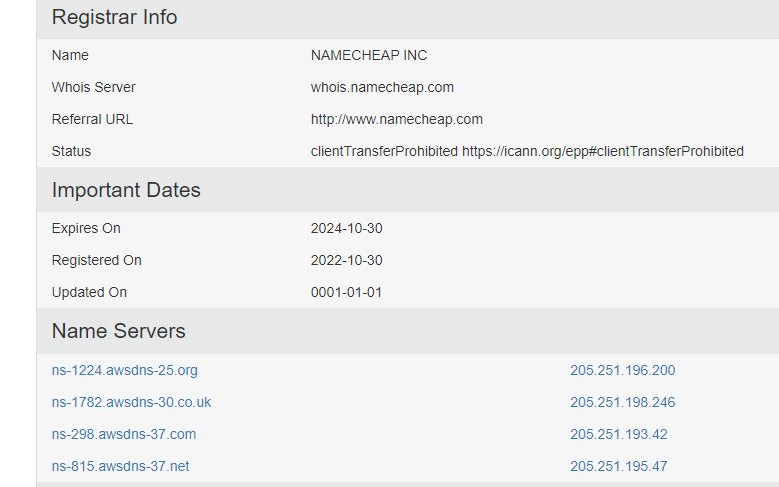
Just overlook rest of the information for now and just focus on the amount of information that is asked. I’m not giving out the answer it’s obvious.
Q2. “Find the website’s source code (repository) on github.com and open the file containing sensitive credentials. Can you find the flag?”
I just misleaded on this one due to the amount of github repos available with that specific name but if this is the problem with you as well just don’t give up and see the answer here try again, you will end up finding the right repo. Rest you can still see what methodology I use to solve this one. Alright, for this one we already have a hint given.

So by reading this it’s obvious we have to search anyone of the three above terms on github to get to the right repo and get the flag. The right term(s) out of all three are “SantaGift” and “SantaGiftShop”, after searching this there are alot of repos that pop up but the right one is https://github.com/muhammadthm/SantaGiftShop . But wait there are alot of files to look for..How are we going to get the flag? This is where experience comes in. So according to me most of the password disclosure vulnerabilities are found in config files and since the config.php file caught my eye.
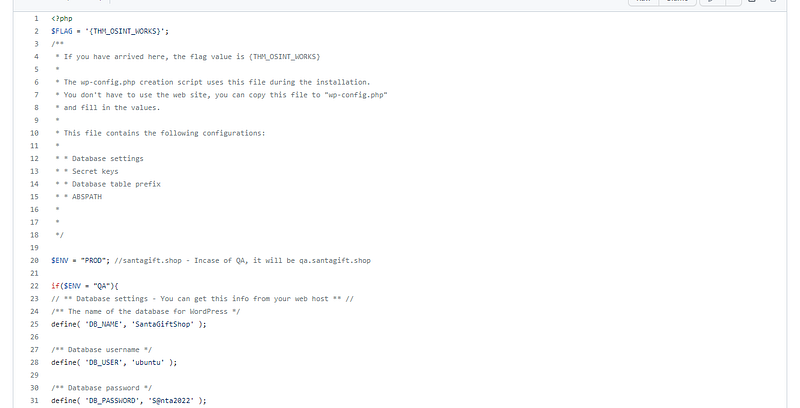
This is how the config.php file looks like after you open it and there you have the flag.
Q3. “What is the name of the file containing passwords?”
Well this one is obvious after the amount of research we just did
Q4. “What is the name of the QA server associated with the website?”
If you analyse all the content in the config.php file you will find that the QA server associated with santagift.shop is qa.santagift.shop
Q5. “What is the DB_PASSWORD that is being reused between the QA and PROD environments?”
This is applicable in alot of real world scenarios as well, since there are alot of developers who forget to remove the passwords inside github repos. But for this question our answer is also in the config.php file (line 31). Come on you can find the password now.
That’s it for this room and I’ll be back with day 4 soon!